01
Authorize
A tenant administrator approves the documented read-only permissions.
Microsoft 365 assessment
Audit Microsoft 365 and Office 365 security: MFA, Conditional Access, administrators, email, sharing, guests, and risky configuration through read-only access.
Request a Microsoft 365 audit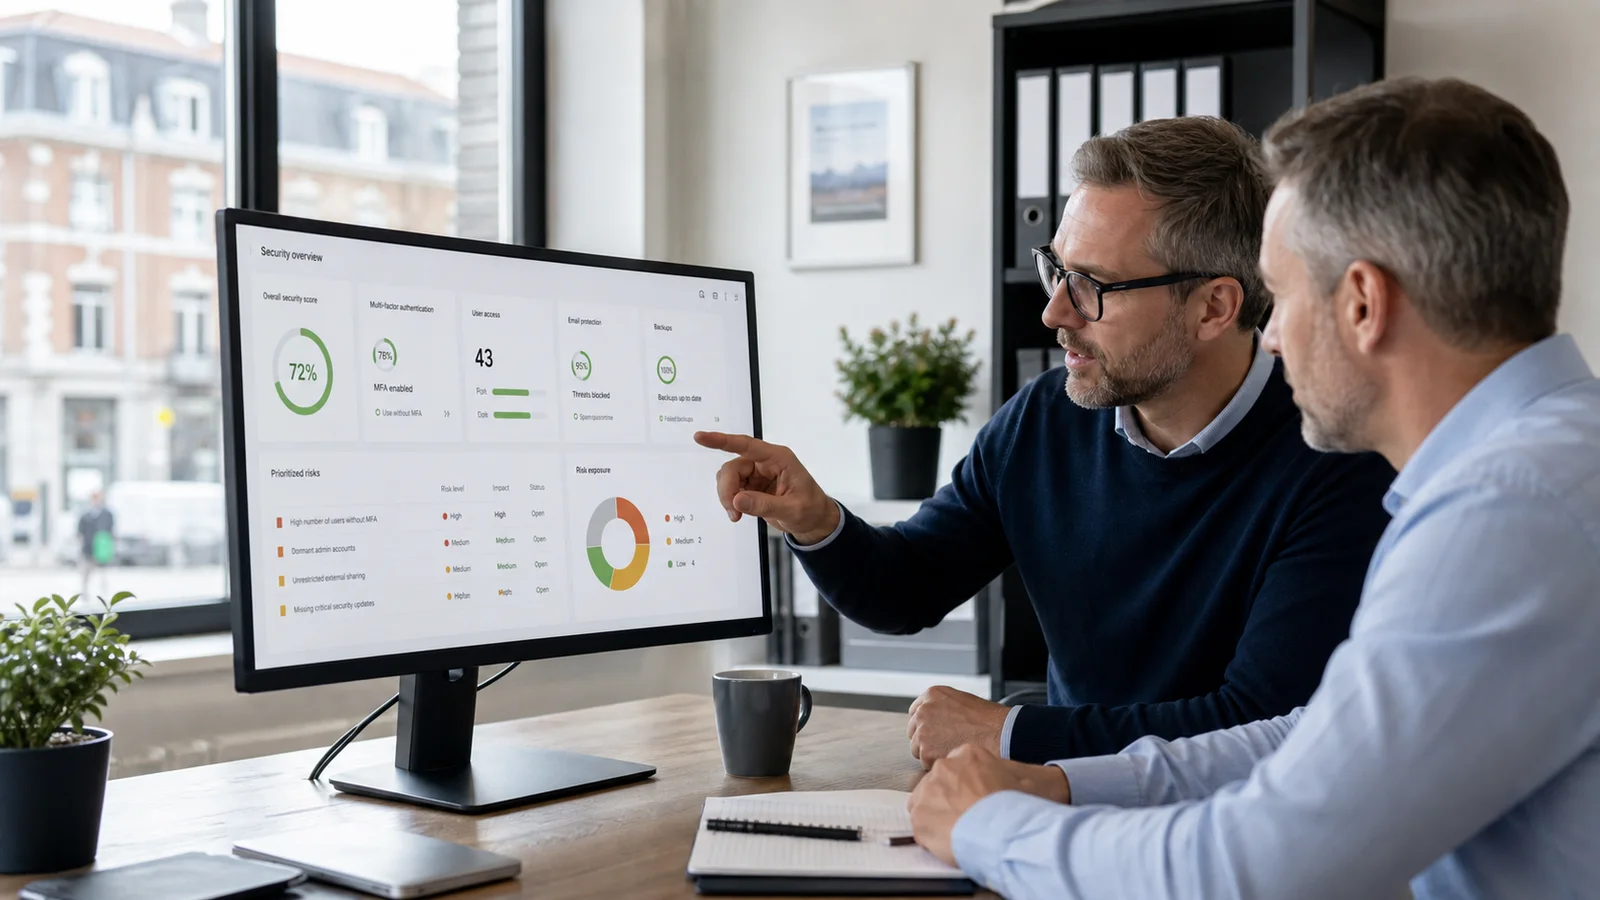
In short
A Microsoft 365 Security Audit checks whether identity, MFA, Conditional Access, administrator roles, email protection, guest access, sharing, and audit settings match the way your company operates. We use explicit tenant consent and the least privileged read access available, then provide evidence, risk, owner, and a prioritized remediation step for every finding.
When this helps
Deliverables
Approach
01
A tenant administrator approves the documented read-only permissions.
02
Configuration and posture data are collected without asking for user passwords.
03
Findings are checked against company size, licences, workflow, and risk.
04
You receive ordered changes, responsible owners, and validation steps.
Clear boundary
The audit does not change tenant settings automatically. Remediation is planned separately, requires approval, and should include testing and rollback for changes that could affect access or email delivery.
No. Access is provided through Microsoft OAuth and explicit tenant-admin consent. Passwords are never shared with us.
For a typical SME tenant, collection and review usually fit within several working days. Timing depends on tenant size, licences, available evidence, and whether interviews or remediation validation are included.
You receive a management summary, evidence-based findings by priority, and a technical action list with recommended owner and validation step. We also explain which recommendations do not fit your licences or way of working.
Yes, as a separately approved remediation scope. We document changes and test important access and mail-flow effects.
Only where relevant posture information is available through the agreed Microsoft services and permissions. A full endpoint assessment is a separate scope.
We will scope the assessment, required access, evidence, review, and expected output before any checks start.
Request a Microsoft 365 audit